
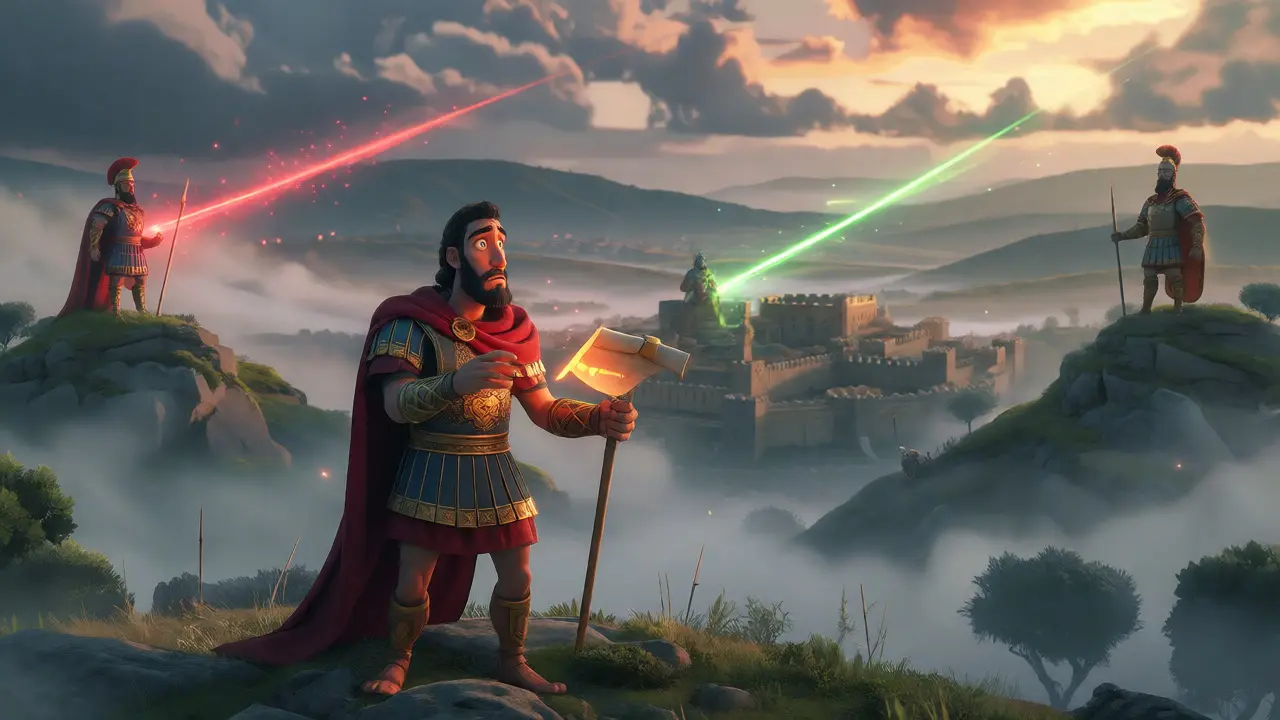
Imagine you’re commanding a division of troops surrounding an enemy city. You need to attack at dawn, but your fellow generals are scattered across different hills. Some might be traitors trying to sabotage the plan by sending false messages. How do you ensure everyone attacks at the same time? This isn’t just a military puzzle; it’s the Byzantine Generals Problem, a foundational concept that explains why blockchains work and why they’re so hard to build.
If you’ve ever wondered how Bitcoin or Ethereum agrees on who owns what without a bank calling the shots, this is the answer. It’s not magic. It’s math. And understanding it changes how you view every decentralized system you use.
The Core Dilemma: Trusting Without Knowing
In 1982, computer scientists Leslie Lamport, Robert Shostak, and Marshall Pease formalized this issue in their paper "The Byzantine Generals Problem." They weren’t writing about crypto yet. They were solving a computing challenge: how can independent computers agree on a single truth when some might crash, lie, or act maliciously?
The analogy is simple. Several Byzantine army divisions surround a city. Each general commands one division. They must decide whether to attack or retreat. Victory requires simultaneous action. If they split, they lose. The catch? Some generals are traitors. They send conflicting orders to different allies. A loyal general receives "Attack" from one source and "Retreat" from another. Who do they trust?
| Failure Type | Description | Consensus Requirement |
|---|---|---|
| Crash Fault | A node stops working but doesn't send bad data. | n > 2f + 1 (Majority) |
| Byzantine Fault | A node sends incorrect or contradictory data intentionally. | n > 3f + 1 (Supermajority) |
This distinction matters. In traditional centralized systems, if a server crashes, you restart it. No harm done. But in a peer-to-peer network like Bitcoin, any participant could try to cheat. They might double-spend coins or forge transactions. The system needs to tolerate these active lies, not just passive failures.
Why Three Times More Nodes Than Traitors?
Here is the mathematical heart of the problem. To reach consensus with up to f traitors, you need at least 3f + 1 total participants. Why three times more? Because each honest general needs to cross-check information from enough sources to identify the liar.
Let’s break it down with numbers. If you have 4 generals and 1 is a traitor, consensus is possible. The 3 loyal generals compare notes. If two say "Attack" and one says "Retreat," the majority wins. But if you have only 3 generals and 1 is a traitor, it fails. The traitor tells General A "Attack" and General B "Retreat." General A hears nothing from B directly, and vice versa. They cannot distinguish between a traitor lying and a loyal general receiving mixed signals. The system stalls.
This rule-n > 3f-is why public blockchains need many nodes. Private blockchains, where members are known and vetted, can sometimes relax this because the risk of arbitrary betrayal is lower. But in open networks, anyone can join. You assume the worst-case scenario: some participants are actively trying to break the system.
Bitcoin’s Solution: Proof-of-Work as a Costly Signal
For decades, this problem remained theoretical. Then Satoshi Nakamoto solved it for open networks using Proof-of-Work. Instead of relying on voting among unknown peers, Bitcoin makes honesty expensive and cheating costly.
Think of mining as a digital lottery ticket bought with electricity. Miners spend real resources (energy and hardware) to solve a complex puzzle. If a miner tries to cheat by broadcasting a fake block, they waste that energy. Other miners see the invalid block and ignore it. The chain grows based on the heaviest proof of work, not just the first message received.
Vitalik Buterin, co-founder of Ethereum, has noted that Bitcoin was the first practical solution to this problem for permissionless networks. It didn’t eliminate the possibility of traitors. It made being a traitor economically irrational. As long as the cost of attacking exceeds the potential gain, honest behavior prevails. This aligns incentives rather than relying purely on technical constraints.
Beyond Crypto: Where Else Does This Matter?
You might think this is just nerd talk for crypto enthusiasts. Wrong. The Byzantine Generals Problem affects critical infrastructure everywhere.
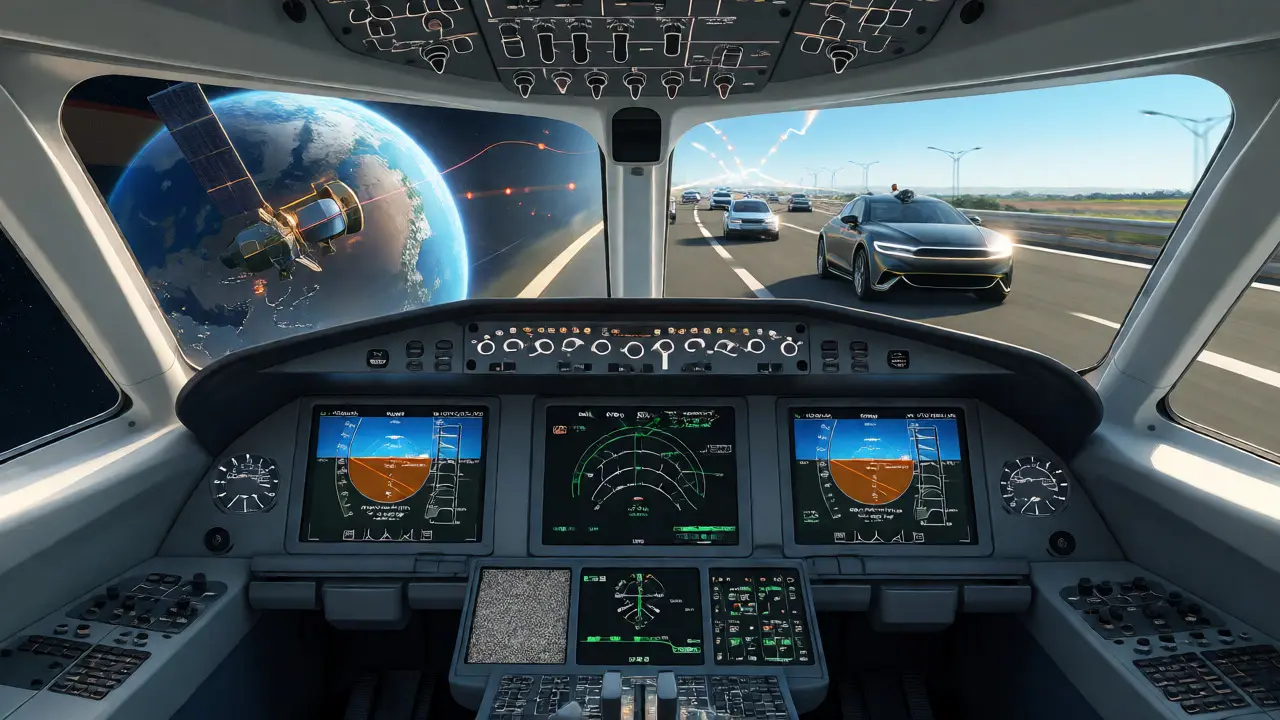
- Aviation: Aircraft control systems often use triple-redundant computers. If one gives wrong data, the other two outvote it. This is classic Byzantine Fault Tolerance (BFT).
- Space Exploration: NASA’s Artemis program mandates BFT configurations for lunar mission computers. A single sensor glitch shouldn’t abort a multi-billion dollar launch.
- Automotive: Modern cars communicate with each other (V2V). ISO 21448 safety standards require protocols that handle faulty or spoofed messages from nearby vehicles.
Anytime you have multiple independent components needing to agree without a central boss, you’re facing this problem. Distributed databases, cloud storage systems, and even smart grids deal with variations of it daily.
Practical Challenges in Implementation
Solving the Byzantine Generals Problem isn’t easy code-wise. Algorithms like Practical Byzantine Fault Tolerance (PBFT), introduced in 1999, work well for small networks but struggle to scale. PBFT requires every node to communicate with every other node. Message complexity grows quadratically (O(n²)). Add more nodes, and the network chokes under its own chatter.
Newer protocols try to fix this. HotStuff, used by projects like Diem (formerly Libra), reduces communication overhead to linear levels (O(n)). Ethereum’s transition to Proof-of-Stake implemented LMD-GHOST, which blends PoS economics with BFT-like finality. These innovations aim to keep security high while letting networks grow larger.
Developers face real hurdles here. A 2022 Stack Overflow survey showed that 78% of distributed systems engineers find understanding BFT requirements a major pain point. Debugging why consensus failed-was it a network lag? A buggy node? A coordinated attack?-takes weeks of specialized study.
The Future of Consensus
We aren’t done solving this. Research continues into quantum-resistant BFT protocols, anticipating threats from future computing power. IBM recently announced Q-BFT, designed to withstand quantum attacks. Meanwhile, enterprise adoption grows. Financial services lead the charge, using private BFT chains for faster settlement times compared to public blockchains.
The core lesson remains unchanged: decentralization costs efficiency. You trade speed and simplicity for resilience and trustlessness. Understanding the Byzantine Generals Problem helps you appreciate that trade-off. It’s not a bug in blockchain design. It’s the price of admission for a world where no single entity controls the truth.
What is the main goal of the Byzantine Generals Problem?
The goal is to achieve reliable consensus in a distributed system where some components may fail or act maliciously. Participants must agree on a single course of action despite unreliable communication channels and potentially dishonest peers.
Why do we need 3f+1 nodes for Byzantine Fault Tolerance?
This ratio ensures that honest nodes can identify and isolate faulty ones. With n > 3f, the number of honest nodes (n-f) is greater than twice the number of faulty nodes (2f). This allows honest nodes to form a majority among themselves, even if faulty nodes try to split them into smaller groups.
How does Bitcoin solve the Byzantine Generals Problem?
Bitcoin uses Proof-of-Work. Miners expend computational effort to validate blocks. Cheating requires redoing all subsequent work, making attacks economically prohibitive. Honest nodes follow the longest valid chain, creating a unified history without needing to trust individual participants.
Is the Byzantine Generals Problem relevant outside of cryptocurrency?
Yes. It applies to any distributed system requiring agreement among untrusted parties, including aviation control systems, space missions, automated trading platforms, and large-scale cloud databases.
What is the difference between Crash Fault Tolerance and Byzantine Fault Tolerance?
Crash Fault Tolerance handles nodes that stop working silently. Byzantine Fault Tolerance handles nodes that continue operating but send incorrect or misleading data. BFT is harder to implement and requires more nodes to function securely.